September 7, 2026
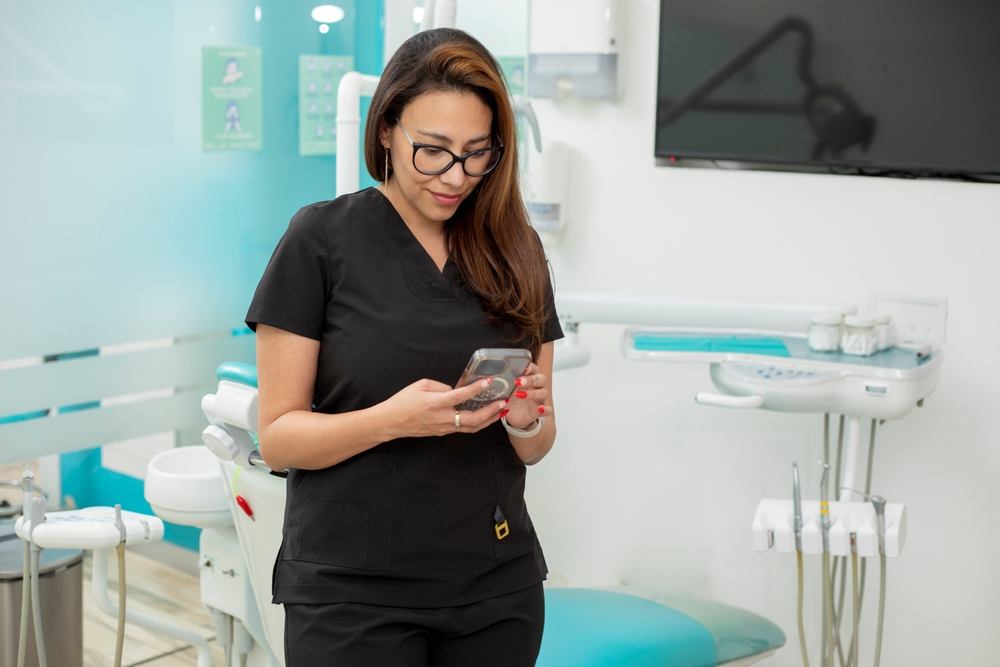 — ✦ —
Personal phones, laptops, and tablets can put dental practice data at risk when they are used to access work email, patient records, scheduling platforms, cloud accounts, or practice-management software. Unlike office-managed equipment, personal devices may not have approved security tools, current updates, encryption, or remote management. If a device is lost, stolen, shared, or compromised, unauthorized users could access sensitive information. Dental practices should control how personal devices connect to business systems and establish clear security requirements for employees.
How Personal Devices Can Put Dental Data at Risk
Employees may use their phones to check appointments, respond to work emails, communicate with coworkers, or sign in to cloud applications. Although this may improve convenience, it also creates access points outside the practice’s direct control. For example, if four employees at a 12-person dental office use personal devices for work, each device may contain saved credentials, email messages, or application access that needs protection.
Lost Devices Can Lead to Unauthorized Access
A misplaced phone or laptop can become a serious security concern if it contains work email, patient messages, downloaded documents, or active application sessions. Strong passcodes, encryption, multifactor authentication, and automatic screen locking can reduce the risk of unauthorized access. Practices should consider requiring devices to lock after five minutes or less of inactivity and instruct employees to report missing devices immediately. When supported, business information and account access should be removable without deleting the employee’s personal content.
Public Wi-Fi and Personal Applications Add More Risk
Personal devices frequently connect to home networks, restaurants, hotels, airports, and public Wi-Fi that the dental practice cannot monitor. They may also contain personal applications that collect data, display aggressive advertisements, request broad permissions, or introduce malicious software. Reused passwords create another concern because a breach involving one personal account may expose credentials used for work.
Simplicity IT’s Cybersecurity and Compliance services can help practices strengthen email security, multifactor authentication, endpoint protection, account controls, and network defenses.
A Personal Device Policy Sets Clear Expectations
Dental practices should have a written policy explaining whether personal devices are permitted, which employees may use them, which systems they may access, and what security settings are required. The policy should cover approved applications, password requirements, software updates, storage restrictions, lost-device reporting, employee departures, and removing business access. Review user permissions every three months, and restrict access as soon as an employee leaves the practice or no longer needs a particular system.
Simplicity IT’s Managed IT services can help practices manage accounts, supported devices, access changes, and routine technology maintenance.
Practice Information Needs Secure Storage and Backup
Patient information, schedules, clinical documents, and important communications should not exist only on an employee’s personal device. Dental practices should use approved business platforms that let them centrally manage, protect, and recover information. Monitored backups and tested recovery procedures can help restore important data after accidental deletion, equipment failure, ransomware, or account compromise.
Simplicity IT’s Backup and Business Continuity services help businesses establish backup schedules, retention periods, recovery priorities, and restore-testing procedures based on their operational needs.
Steps That Can Improve Personal Device Security
Dental practices can reduce risk by limiting personal device access to employees who require it, requiring multifactor authentication, separating work information from personal content, and preventing local storage of patient information whenever practical. Employees should use supported operating systems, install important security updates promptly, avoid unsecured networks, and report suspicious login requests or phishing messages immediately. Regular access reviews, employee training, and consistent offboarding procedures can help prevent former employees, unused accounts, or outdated devices from retaining unnecessary access.
Manage Personal Devices With a Clear IT Strategy
Every dental practice has different employees, applications, workflows, and technology requirements. Simplicity IT helps dental practices review personal device use, secure employee accounts, implement multifactor authentication, manage access permissions, monitor supported systems, and prepare for data loss or cyber incidents. Simplicity IT provides technical services that can support a practice’s HIPAA security responsibilities, but does not provide legal advice, perform formal compliance certification, or guarantee that technology controls alone make an organization HIPAA compliant.
Improve Security Across Your Dental Practice
Personal devices can support convenient access, but they should not create uncontrolled pathways to patient or business information. Simplicity IT provides healthcare-focused managed IT, cybersecurity, backup, access management, and technology planning for dental practices throughout San Diego County. Contact Simplicity IT to review personal device use within your practice and identify practical ways to strengthen security. Schedule your Discovery Call here.